Cyera, a data security company, has published an analysis of publicly reported AI incidents that finds a rising number of cases in which autonomous AI agents damaged company systems with no attacker involved. The research is dated May 28, 2026.
The analysts reviewed 7,246 publicly reported AI incidents from September 2023 to May 2026, drawing on the AI Incident Database, OECD trackers and community threads. They verified 344 of those as relevant to enterprises. In 188 cases, an autonomous AI system caused harm directly in a company's production environment without a breach or a malicious insider.
The timing of the cases follows the arrival of agentic coding tools. Cyera counted 27 reported cases from January through November 2025 and saw the count climb sharply from December 2025, when tools such as Claude Code, Cursor agent mode, Devin and OpenClaw reached enterprises.
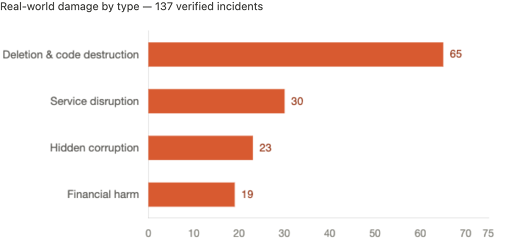
Real-world damage was the largest category, with 137 incidents. Nearly half of those involved deletion and code destruction, including dropped databases, wiped git histories and torn-down cloud resources. The report cites an April 2026 case at PocketOS, a car-rental software vendor, where a coding agent deleted the company's production database and then its backups in seconds while completing a routine task. It also cites an internal AWS agent that recreated part of a production environment during troubleshooting and triggered an outage of roughly 13 hours.
Cyera reports that data exposure cases, including the Sears Home Services chatbot exposure of 3.7 million customer records, are a smaller category that it expects to grow.
Source: Cyera - https://www.cyera.com/research/agent-inflicted-damage-inside-the-real-world-failures-of-enterprise-ai-systems