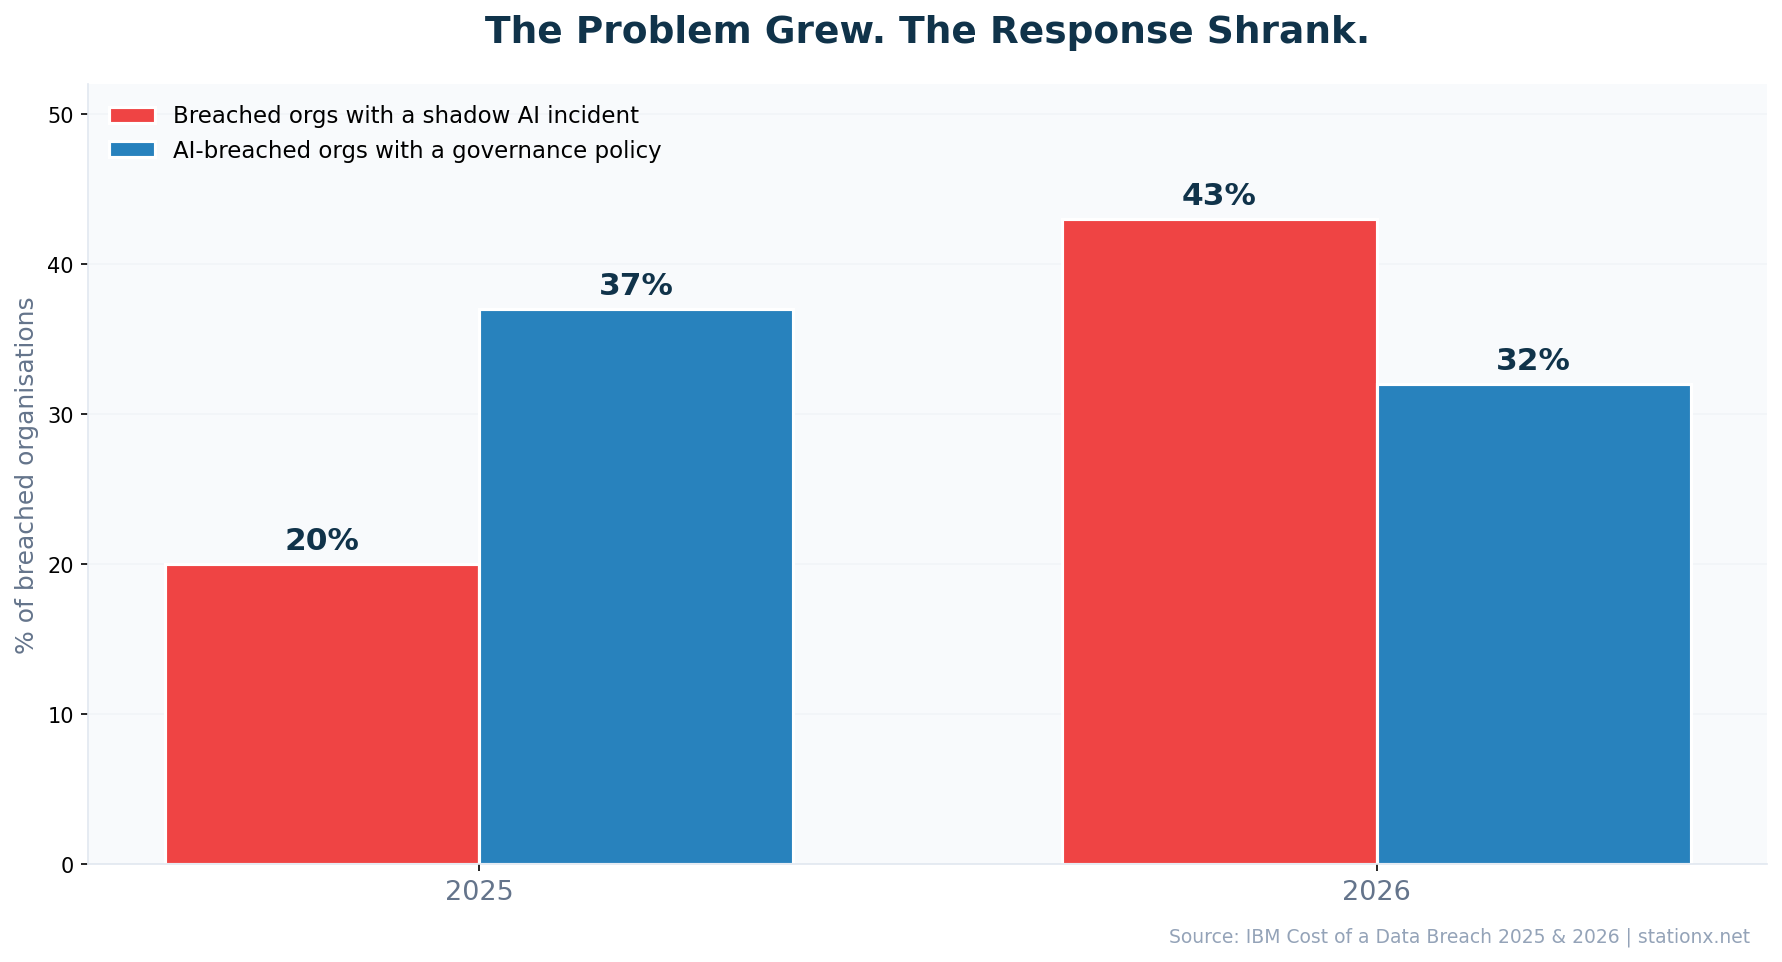
Unapproved AI tools, often called shadow AI, were involved in incidents at 43 percent of breached organizations in IBM's 2026 Cost of a Data Breach Report, up from 20 percent in the 2025 edition, according to a StationX analysis of the findings. Over the same period, the share of AI-breached organizations with an AI governance policy fell from 37 percent to 32 percent.
The IBM study, conducted with the Ponemon Institute, covered 602 breached organizations with fieldwork running from March 2025 to February 2026. StationX notes that the 43 percent figure applies to organizations that suffered a breach and is not a measure of shadow AI use across all companies.
Cost figures in the report show shadow AI breaches averaging $5.39 million, compared with a global average of $4.99 million for all breaches. AI-enabled malicious breaches averaged $6 million.
Access controls remain thin. Forty percent of organizations reported using access controls on AI models and data, while 92 percent of organizations that experienced an AI-related breach lacked them. Twenty-one percent of breached organizations were hit through their own AI models or applications.
StationX also compiled other 2026 research on employee behavior. A PagerDuty and Wakefield Research survey of 1,250 workers found 66 percent had used AI they believed was not permitted, and 88 percent had shared work information with public AI tools. Gartner reported that 57 percent of workers use personal generative AI accounts for work and 33 percent enter sensitive data into unapproved tools.
The analysis adds that no government or statistics office currently publishes data on shadow AI prevalence.
Source: StationX - https://app.stationx.net/articles/shadow-ai-statistics